Cisco SDA architecture still has a core, an edge and a way out to the rest of the world, but the roles have new names and the logic underneath has changed. In this blog, we'll compare the traditional three-tier network with the Cisco SD-Access fabric and show how each layer maps across.
SDA Architecture: What Changes From a Traditional Network?
 Cisco Software-Defined Access (SD-Access, or SDA) splits the campus network into a physical underlay and a logical overlay, managed from Cisco Catalyst Center. The cabling and switches look much the same as before. What changes is the role each device plays and how traffic and policy move across the fabric.
The underlay is a routed network that simply moves packets between fabric devices. The overlay is the "software-defined" part: virtual networks built on top of the underlay, with users and devices placed in them by identity rather than by the switch port they happen to plug into.
We've covered the fabric itself in What Is Cisco SDA Fabric?. This post focuses on the architecture: which device does what, and how that lines up with the network you already run.
Three-Tier Design: How Traditional Networks Are Built
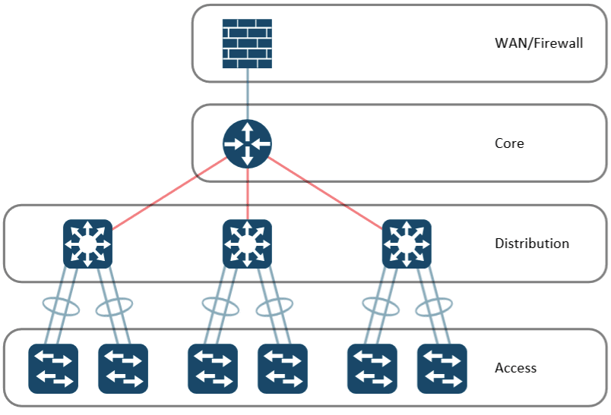
Most enterprise networks still follow the three-layer model: core, distribution and access. Layer 3 routing usually terminates at the core, and Layer 2 VLANs are extended down through distribution to the access switches where users connect. It has stood the test of time, and it's in every Cisco Press book (yes, we've read a few).
Core: where Layer 3 typically terminates and the routing protocols run.
Distribution: Layer 3 in larger designs; often Layer 2 only (VLANs) in smaller ones.
Access (edge): usually Layer 2 only, where all the endpoints connect.
In smaller networks, the core and distribution layers are often combined into one, known as a collapsed core design. A WAN router or firewall sits alongside, linking switch blocks with different security levels and providing the internet connection.
The diagram below shows this classic high-level design.
The weakness isn't the hierarchy itself. It's the large Layer 2 domains stretched across it, and the legacy protocols needed to keep them loop-free and resilient.
Fabric Roles: Border, Control Plane, Edge and Extended Nodes
 In a Cisco SDA fabric, each device is given a role. Border nodes connect the fabric to the outside world, control plane nodes track where every endpoint is, edge nodes connect endpoints, and extended nodes stretch the fabric to smaller switches. Layer 3 is pushed right out to the edge.
That shift to Layer 3 is the big change. The extensive Layer 2 designs of traditional networks give way to a routed fabric, so many of the legacy Layer 2 protocols are no longer needed, and you gain much more granular control and mobility.
The diagram below shows the base building blocks of an SDA fabric design.
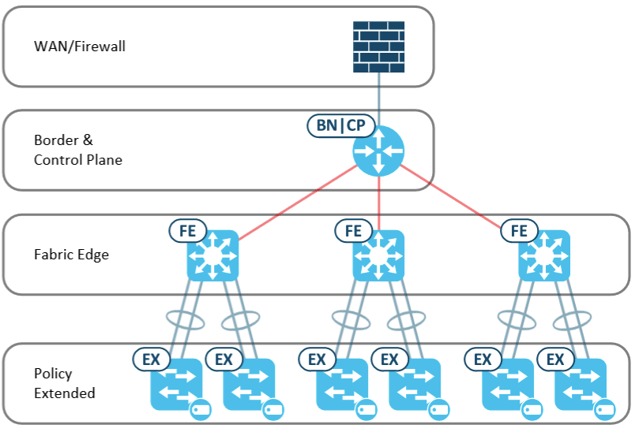
Control Plane Node
The control plane node is the brain of the fabric. It keeps the map of which endpoint sits behind which edge node, so traffic can be sent straight to the right place.
Border Node
Border nodes are the way in and out for all fabric traffic. Think of them as the perimeter of each fabric site, connecting it to the WAN, the data centre, the internet or a traditional network. In many designs the border and control plane roles run on the same pair of devices.
Edge Node
Edge nodes are where endpoints connect. Each edge node acts as an anycast default gateway, so the gateway looks the same to a device wherever it plugs in across the campus. That's what lets the fabric behave like one large switch while still being routed underneath.
Extended and Policy Extended Nodes
Endpoints can connect directly to an edge node, or through an extended node. Extended nodes work like traditional Layer 2 access switches hanging off the edge. Policy extended nodes add the ability to enforce Cisco TrustSec group-based policy locally, so segmentation still applies at the furthest reaches of the fabric.
Role Mapping: How Traditional Layers Map to the Fabric
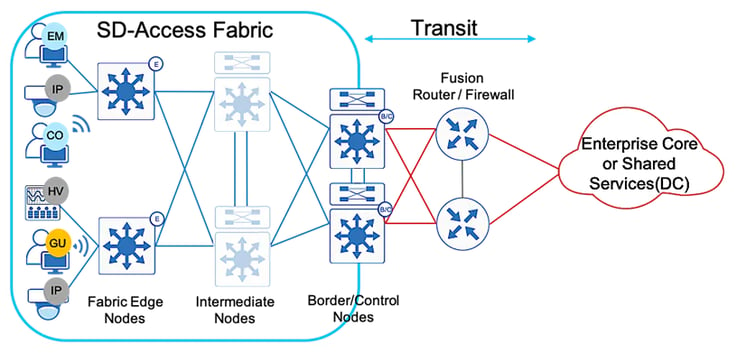
Each SDA fabric role lines up with a traditional layer. The core becomes the border and control plane, the access layer becomes the fabric edge, and smaller downstream switches become extended or policy extended nodes. That one-to-one mapping is what makes a staged migration to SD-Access practical.
The physical view shows that the boxes and cabling barely change.
The logical view is where the difference shows: the routed underlay with the fabric overlay running on top.
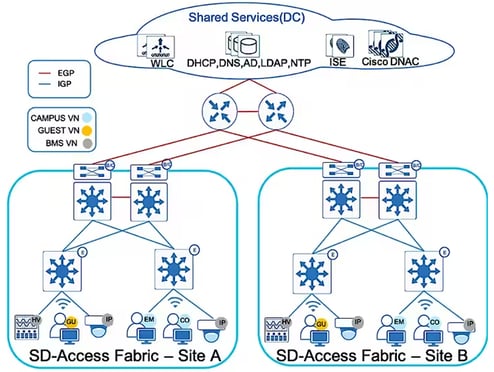
In smaller networks, all of these roles can be shared by one device or split across a handful of devices. In large networks, key roles such as border and control plane are spread across multiple devices for redundancy and scale.
Cisco SDA Architecture: FAQs
What Is Cisco SDA Architecture?
Cisco SDA architecture is the design model behind Cisco Software-Defined Access. A routed underlay carries a logical overlay, managed from Cisco Catalyst Center, with devices given fabric roles: border, control plane, edge and extended nodes. It replaces large Layer 2 domains with Layer 3 and identity-based policy.
Does SD-Access Replace the Core, Distribution and Access Layers?
Not physically. The hierarchy and cabling largely stay as they are. What changes is the role each device plays: the core typically becomes the border and control plane, the access layer becomes the fabric edge, and Layer 3 moves out to the edge.
What Is the Difference Between an Extended Node and a Policy Extended Node?
Both extend the fabric to switches beyond the edge, much like a traditional Layer 2 access layer. A policy extended node can also enforce Cisco TrustSec group-based policy itself, so segmentation applies right where the endpoint connects.
Can One Device Run All the Fabric Roles?
Yes, in a small site. The border, control plane and edge roles can all run on one device, or be split across a handful. Larger campuses spread the border and control plane roles across multiple devices for redundancy and scale.
Cisco SDA Architecture: Summary
Traditional and SDA architectures map closely to each other. The protocols are different and Layer 3 reaches much further, but you still need edge devices for endpoints and interconnect points to the rest of the world. Learning the new terminology takes a little while, and understanding the mapping makes the move to SD-Access far easier to plan.
Need Help With Cisco SD-Access?
Our Cisco SDA Fabric team can map your current network to a fabric design and plan a staged migration with Cisco Catalyst Center. Our Catalyst Center Enablement service is a good place to start. If that's useful, get in touch with the IPTel team or email sales@iptel.com.au.